Security and file handling for OCR uploads
A practical account of where an uploaded file goes, which copies remain, how access is limited, and what users should decide before sending sensitive material.
- Guest exports
- 60 minute local expiry
- Account exports
- 30 day local expiry
- Transport
- HTTPS in production
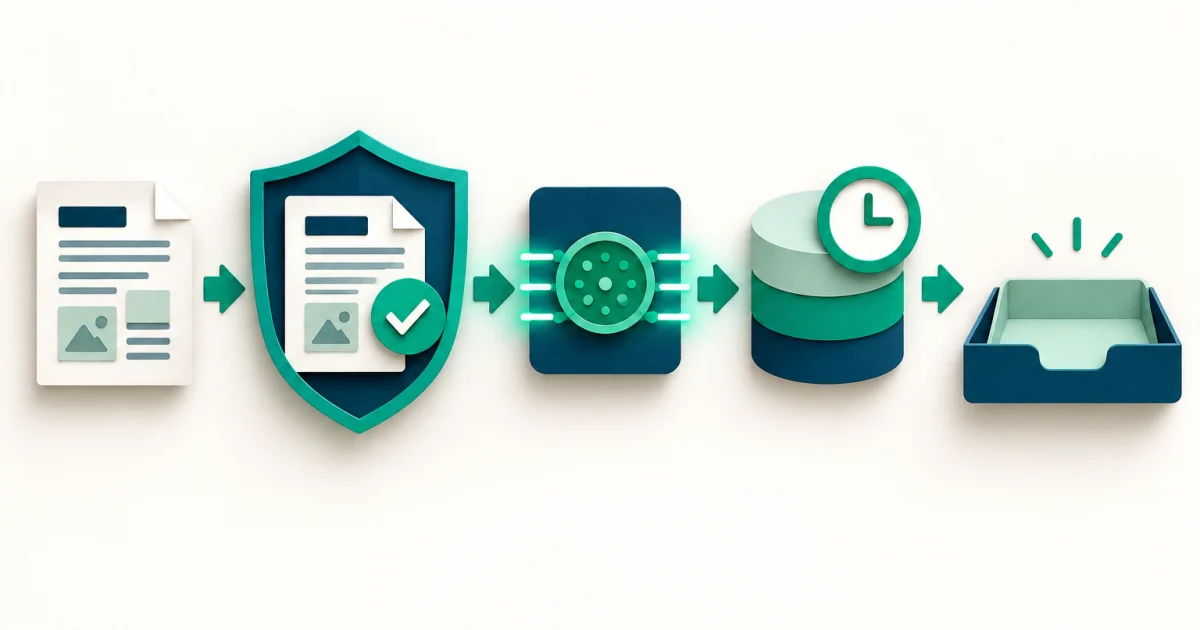
The OCR file lifecycle
A file can create several copies for different purposes. Each is accounted for here.
- 1
Validate
The server checks the extension, actual image or PDF signature, upload limit, pixel count, and selected page range.
- 2
Prepare locally
A random request directory holds the source, rendered pages, and cleanup copies needed for the job.
- 3
Recognize
When remote OCR is enabled, a prepared image or selected PDF pages are sent to the configured processor over HTTPS.
- 4
Build exports
Text, diagnostics, and requested document formats are written to the local result directory.
- 5
Remove and expire
The local working directory is removed when processing finishes. Result exports expire on their stated schedule.
Local and remote trust boundaries
A local expiry is not a claim that a separate processor has deleted its copy.
| Location | What it may contain | How it is handled |
|---|---|---|
| Local working directory | Untouched upload, prepared images, rendered PDF pages | Random per request and removed when the job succeeds or fails |
| Local guest result | OCR text and generated exports, including source page images in layout-preserved formats | Available through an unguessable token for 60 minutes |
| Local account copy | Generated exports saved by a signed-in user | Private to the account for 30 days or until user deletion |
| Remote OCR processor | A prepared image or selected PDF pages and recognition output | Subject to the processor's own storage and access terms, not the local expiry timer |
Controls used by the application
Security is a set of boundaries, not one badge or one header.
Upload validation
Supported extensions are allow-listed, image contents must match the extension, PDFs must have a PDF signature, and decompression-bomb limits bound image pixels.
Bounded processing
File size, PDF page range, remote request size, timeouts, retry counts, and image dimensions are constrained to reduce resource abuse.
URL and redirect checks
Remote OCR status requests must stay on the configured origin. Cross-origin redirects and non-HTTPS production service URLs are rejected.
Browser protections
Production responses use a content security policy, clickjacking protection outside embeds, MIME sniffing protection, a restricted permissions policy, and HSTS.
Account ownership checks
Saved account exports require the signed-in owner. State-changing account forms use a CSRF token and session cookies are HTTP-only.
No public result index
Processing, result, download, share, account, and workflow routes are marked noindex and excluded from public sitemap discovery.
Before uploading a sensitive document
No online OCR service is the correct default for every file.
- Confirm you have authority to process every person's information in the file.
- Remove pages, margins, identifiers, or attachments the OCR task does not require.
- Check legal, contractual, professional, workplace, and residency requirements.
- Decide whether remote processor retention is acceptable before upload.
- Use locally managed OCR when you need direct deletion control or a closed network boundary.
Use the online OCR privacy checklist for a document-by-document decision.
What this page does not promise
Transparent controls are not a formal certification.
This page describes controls implemented by the current application. It does not claim an external security audit, penetration-test certification, regulatory attestation, zero risk, or guaranteed availability. Administrators may have infrastructure-level access required to operate and recover the service; routine human reading of uploads is not part of the product.
Free-OCR.net does not use uploaded document contents to train its own OCR models. Remote processing remains governed by the remote provider's policies and controls.
Page reviewed 25 October 2026